Code Monger, cyclist, sim racer and driving enthusiast.
10321 stories
·
6 followers

Switching Password Managers in 2026

2 Shares

Important Note: Although I work at Apple in the password management and app/website authentication spaces, in this post I am speaking only for myself, personally. There is no “news” in this post or any kind of “inside scoop”. Please do share this post, but if I see “Apple’s Ricky Mondello” anywhere, I’ll be sad. My intention is to help people benefit from data portability and interoperability work I’ve personally participated in. Nobody should feel locked into their password manager. :)

Would you believe me if I told you that the best device to switch password managers on might be your iPhone or iPad? For many pairs (exporter and importer) of apps, it’s true! Here’s a simultaneously boring and exciting video of me exporting 100 items from 1Password and into Apple Passwords.

To export from 1Password’s iOS app, navigate to Items › Settings › Advanced › Start Export. After approving the export, an iOS system interface confirms the data transfer request with Face ID and has me select the destination app. I pick “Passwords” (Apple Passwords), confirm my selection, and then Passwords opens to import the data. The data that’s exported from 1Password and imported to Apple Passwords includes passwords, passkeys, verification codes, notes, and more. No data is deleted from 1Password as part of the export.

Apps that support this mechanism include Apple Passwords, 1Password, Bitwarden, Dashlane, DuckDuckGo, Devolutions, and more.

You might be wondering how a mobile operating system (of all places!) got data interoperability for password managers that’s easier, more secure, and more comprehensive than on desktop.[1] You can thank passkeys and the passkey community for this. (But wait — didn’t you read on X or Hacker News that passkeys are just a trojan horse for platform and password manager vendor lock-in? Weird!)

I gave a keynote at the Identiverse conference this last June that, in part, tells the story of how delivering data interoperability for passkeys necessitated a bunch of standardization and innovation that’s made the password manager interoperability story better for everyone. (Here’s a timestamped YouTube link to the relevant portion, starting at 24:48.)

Transcribed, the story:

Back in 2022, when passkeys were first made available on iPhone, one of the most important bits of feedback that the community gave Apple was: “Are these my credentials? My credentials that I can move between apps like passwords and a password manager? Or are they locked to wherever I initially saved them?” The answer to this was easy. Your credentials are yours to take and manage in whatever software you want, on whatever platform you want, whenever you want.

We just needed to figure out how to enable that in a phishing-resistant way. At the time, the state of the art for transferring credential data wasn’t great. I’m talking about manually exporting an unencrypted file and then importing it into another app. And I think you all know that was going to be a non-starter for passkeys because a threat actor could trick someone into exporting their data and then uploading it to them. That’s called phishing.

For data interoperability for passkeys to maintain their phishing-resistant promise and their ease of use, we were gonna need to work together and innovate as an entire community. And so, some folks within the FIDO Alliance started working on a concrete data format and requirements around transfer. In May of 2024, the first draft of the Credential Exchange format was published.

That format, which is now published as an open spec that anyone can read, covers not just passkeys, but all of the rich data that you’ll find in a modern credential management app. At Apple, we started building on top of that work. And as of iOS 26 and macOS 26 released last fall, passkeys are now securely transferable between credential manager apps on Apple’s platforms. And that’s through a first-class mechanism that was built specifically for those apps.

Here’s how it works. In the first app, you select the data that you want to export, and then you initiate a system export. In a secure, isolated, and out-of-process picker, you choose which of the registered other apps you want to transfer that data to. Then you Face ID, and you’re done. The data is transferred directly between the two apps that you have trust of, without any intermediate files being created.

Then What?

A data transfer starting on an iPhone or iPad is genuinely a fantastic start, but I recommend thinking about switching password managers as a process. You can use the relatively rare and potentially disruptive event of switching password managers as a reason to clean house a bit. Back in September of 2024, I wrote a piece titled “Consider Slowing Down When Switching Password Managers” about this, but I’m going to summarize and update my advice in this post so you don’t have to go back and read that one.

My tips:

  1. If you’re fortunate enough to be able to, upgrading your phone is a great time to switch password managers! Many apps will, annoyingly, make you re-sign in. You can use that as an opportunity to stress test your new setup. You might also be in a mood to rearrange your apps, refresh your settings, and generally tidy up. I recommend you:
    1. Do your bulk transfer from your old app to your new app on your existing device, as described above, before you get your new device.
    2. Going forward, treat your new app as the source of truth for your information, and only consult the old app if something goes wrong. Do not spend time updating or deleting information from the old app; it’s only there as a safety net. Don’t try to keep multiple password managers in sync; with today’s technology, that’s folly.
    3. On your existing device, turn on AutoFill for your new app and turn off AutoFill for your old app. You’ll have a much better experience if you’re not having nearly identical suggestions duplicated from two apps.
    4. When you get your new device, let iOS copy your content and settings from your existing phone to your new one. Whether you do that or not, check to ensure that your data transferred in both your new and old apps, and then ensure AutoFill is only enabled for your new app.
  2. Wait as long as you can[2] to delete the exporting app and its contained data, which now serves as a backup. Although the data interoperability standard smooths over incompatibilities, software is still software. Deleting your old app could feel good, but you’re throwing away an important backup. Do stop paying for your old app whenever you’re able to, but don’t delete your account. Again, safety net.
  3. If you have time, visit the apps and websites that you have credentials saved for and log in to check if your account is still in good standing. If your password has any security issues, generate and save a new strong password, and then see if you can enable a passkey, or failing that, a verification code generator. You’ll sometimes learn that a website doesn’t exist anymore!

If You’re Switching to Apple Passwords

Here are a few things you might want to know:

  1. The Passwords app gets bug fixes, enhancements, and new features with Apple OS releases, so try to run the latest versions of those operating systems to make sure you’re not missing out. If you haven’t updated to macOS Tahoe yet, macOS Golden Gate’s Passwords app is a pretty big leap forward from version 1.x on macOS Sequoia!
  2. The app supports shared groups (like, a shared folder) and has password histories. The app does not support custom fields, although there is a single notes field on every item.
  3. When adding something new to Passwords, both a user name and password are optional. You can have an item that’s just a title and a note! For richer secure notes, Apple’s Notes app is great.
  4. The Mac app has a menu extra that can be enabled in the app’s settings. It’s handy!
  5. The Mac app supports AutoFill in non-Safari browsers with the iCloud Passwords browser extension. In the app’s “Passwords” menu, select “Get Browser Extension…” to see a list of your installed browsers with links to install the extension in that browser. (Fun fact: the data that powers this view is an open source JSON file.)
  6. The app has a Security tab that tells you about passwords that are weak, reused, or have appeared in a data leak. It’s similar to 1Password’s Watchtower feature, but is powered by an Apple service.
  7. Apple Passwords is available on Windows by installing iCloud for Windows. This link is also in the Help menu of the Mac and iPad apps.
  8. The Passwords app unlocks using Face ID, Touch ID, or your device passcode or Mac login password. You cannot set a different “master” password.
  9. Exporting your data from Apple Passwords works completely offline using the data present on your device. You don’t have to be signed in to an Apple Account.

About Values

I genuinely don’t care a lot about what password manager people use[3], but it’s important to me personally that people have ownership of their data and never feel locked into software. The now-legacy password manager data portability experience served as a user experience moat around software and was a non-starter for both passkeys and everyday computer users.

At a FIDO Alliance meeting in May of 2023, when folks from 1Password and Dashlane were demonstrating a proof of concept for transferring credential data from one app to another, I recommended breaking the data format and transport layers into two different work items, and my recommendation was adopted. The data format became the Credential Exchange Format, which is transformed into Swift structs for strongly-typed and versioned data interoperability on iOS, iPadOS, and macOS. I’m happy with how a collaboration on a data portability standard married nicely with an operating system capability, and it makes me happy to be able to directly contribute to work that aligns with my values.

1Password’s recent investment in the Omarchy Linux distribution, created by the outspoken and dangerous David Heinemeier Hansson, and the subsequent industry conversation, inspired me to “fast”-track publishing updated advice on switching password managers. This investment was justifiably criticized by many, including employees of 1Password. I feel for those employees because it’s a terrible feeling when the impact of your work is diminished by actions you had no say in and can’t control.

In this moment, where we’re globally reckoning with the influence of regressive ideas, organized far-right extremists, and the bottomless pockets of the ultra-wealthy, many people appreciated the ability to express their disappointment and freely move their data between password manager apps. Technology is not and has never been morally neutral or exempt from moral consideration.


  1. This OS-facilitated secure data transfer capability exists on macOS, and Apple Passwords supports it. 1Password and some other apps haven’t adopted it there yet.  ↩

  2. I personally switched away from 1Password and to Apple Passwords about ten years ago, but I still have an old copy of 1Password running on one of my Macs. I admit that this may have been easier to do before the advent of subscription software!  ↩

  3. You know, as long as it has a good track-record of responding to security issues.  ↩

Read the whole story
LeMadChef
13 hours ago
reply
Denver, CO
acdha
29 days ago
reply
Washington, DC
Share this story
Delete

Radioactive Health Hoax from the 1920s Returns

1 Comment and 2 Shares

Daily Fact Check from NewsGuard AI

Did Trump announce the end of the Iran war and declare “total victory” this month?


Popular Health Influencer Promotes Radioactive Water, a Long-Discredited, Dangerous Health Hoax

By John Gregory

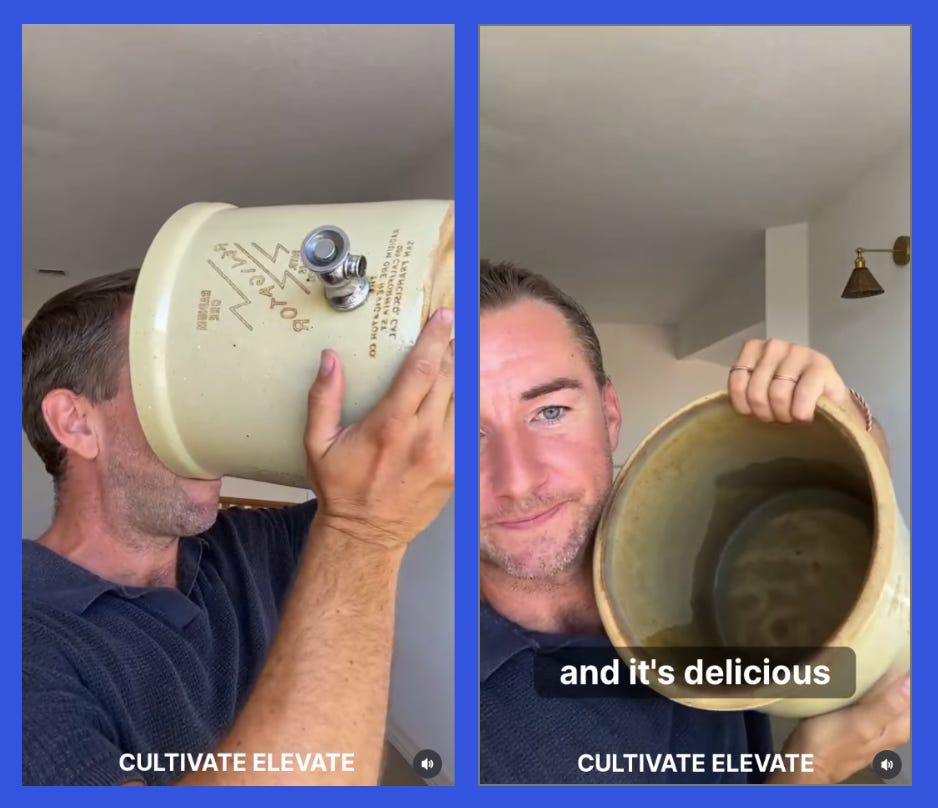
Matt Roeske, owner of the Cultivate Elevate supplement company, drinks from a radium water jug as he promotes the radioactive element as a solution to all health ailments. Source: Instagram account @cultivateelevate

What’s happening: Spurred on by a popular health influencer, social media users are claiming that exposure to the radioactive element radium in drinking or bathing water is safe and actually provides health benefits, a dangerous false claim that was discredited nearly a century ago.

Context: Bathing in water containing radium or consuming products with radioactive water was baselessly promoted as a cure-all beginning in the 1920s.

  • One method of consuming radium water was irradiating water at home in ceramic jugs lined with radium and uranium. Companies that sold the jugs promised that they could “remove cellular poisons,” according to a 2010 press release by the U.S. National Institute of Standards and Technology, or NIST.

A closer look: The false claim has been resurrected, thanks to Matt Roeske, a health influencer and owner of Arizona-based supplement company Cultivate Elevate.

  • In a Sept. 24, 2026, video posted on the Cultivate Elevate Instagram account, which has 501,000 followers, Roeske drank from what he said was a vintage 1920s radium water jug, saying radium water was “perfectly harmless” and could “heal every single ailment.” The caption on the video stated, “Radioactive Radium Water healing all in 1929.” The video received 170,000 views and 10,700 likes in five days.

  • Roeske posted the video the same day on X, where he has 121,000 followers, receiving another 281,000 views and 6,800 likes. An Urdu-language X account, @Pro_truthseeker, reposted Roeske’s video on Sept. 25, receiving 15,000 views and 52 likes.

Actually: Exposure to high levels of radium can cause severe health effects, including anemia, cancer, and death, according to the U.S. Agency for Toxic Substances and Disease Registry.

  • A 2010 NIST study tested the same brand of vintage radium water jugs seen in Roeske’s video and found that the water contained high levels of radon — the gas formed as radium decays — and also toxic levels of arsenic and lead.

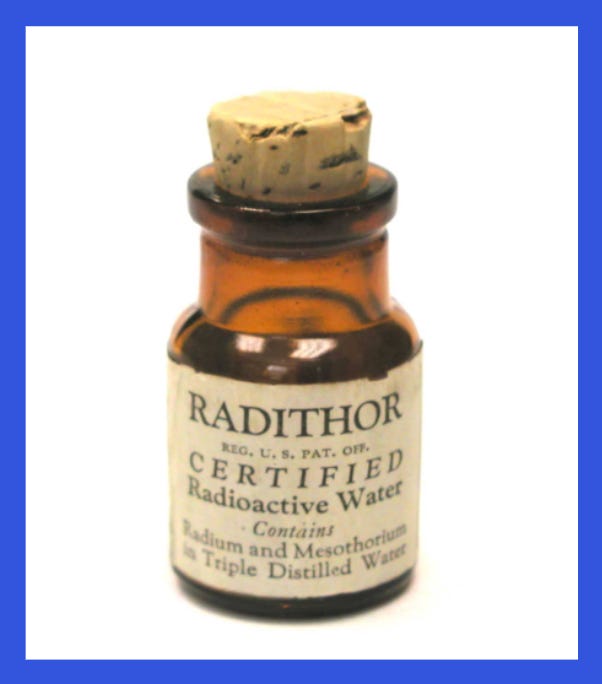
Another radium water product from decades ago, Radithor, was described by its manufacturer to be “harmless in every respect” and a cure for diabetes, heart disease, and “sexual decline,” among other conditions, according to a 2008 document produced for the U.S. Nuclear Regulatory Commission by the Oak Ridge Institute for Science and Education in Tennessee.

Radithor was sold in the 1920s as “harmless” radioactive water to treat a range of ailments. Source: Oak Ridge Institute for Science and Education in Tennessee.
  • The dangers of radium water consumption gained national attention in 1932 when wealthy socialite and industrialist Eben Byers died from jawbone cancer caused by years of consuming Radithor. A 1932 Time magazine article described Byers’ condition before his death, saying that most of his teeth and jaw had been removed and “the remaining bone tissue of his body was slowly disintegrating and holes were actually forming in his skull.”

  • In a Sept. 26 Instagram video, Roeske claimed that Byers’ death “was a make-believe story” meant to suppress the health benefits of radium water.

  • In response to a NewsGuard email seeking comment from Roeske, a Cultivate Elevate customer support representative did not comment on the health claims and instead sent NewsGuard links to two other Roeske videos about radium water.

Zooming out: The U.S. Food and Drug Administration’s website cites the dangers of radium water products, particularly Radithor, as one of the motivating factors behind a push to expand the agency’s authority in the 1930s.

  • These efforts eventually resulted in the passage of the Food, Drug, and Cosmetic Act of 1938, which remains in effect today, requiring all new medications to go through an approval process to prove they are safe before being sold to consumers and prohibiting companies from claiming their products cure ailments without supporting scientific evidence.


Want to learn more? Try NewsGuard AI.


Become a Reality Check Premium Member and get NewsGuard AI for free. Click here.


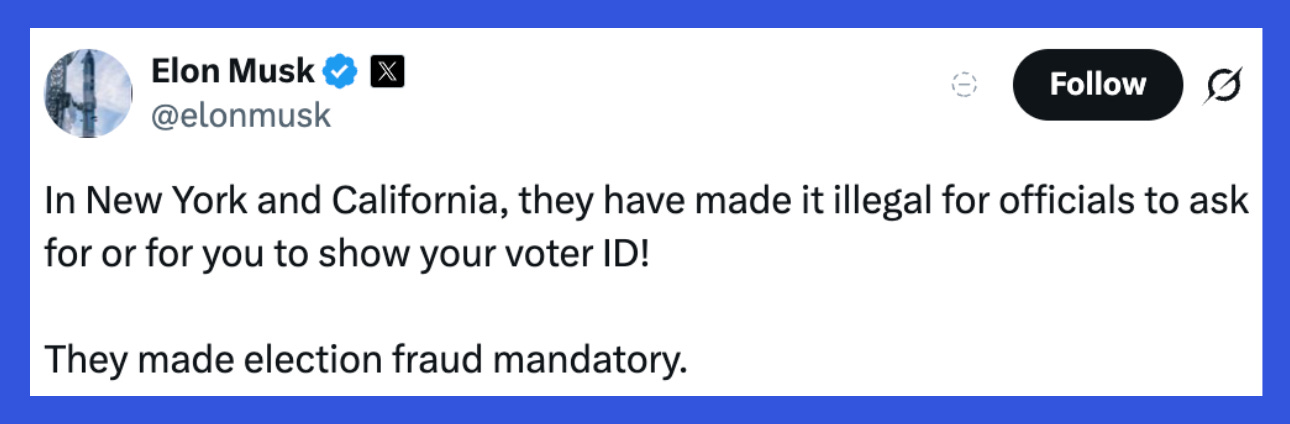
Midterms Watch: Elon Musk Falsely Claims that Requesting a Voter ID in New York and California Is “Illegal”

By Aron Ouzilevski

Elon Musk falsely claims that asking for voter ID in New York and California is “illegal.” Source: X account @elonmusk

What’s happening: X owner Elon Musk and other pro-Trump social media users are falsely claiming that New York and California have made it illegal for poll workers to ask voters for ID, thus making election fraud what Musk called “mandatory.”

A closer look: On Sept. 27, 2026, Musk wrote on X: “In New York and California, they have made it illegal for officials to ask for or for you to show your voter ID! They made election fraud mandatory.” The post received 6.5 million views and 100,000 likes in one day.

  • The next day, pro-Trump commentator Eric Daugherty, chief content officer of the Florida-based conservative news outlet Florida’s Voice, posted: “NOW: Elon Musk just sounded the alarm to millions of Americans that New York and California ‘made election fraud MANDATORY.’ In New York and California, they have made it illegal for officials to ask for or for you to show your voter ID!’” The post received 155,600 views and 5,600 likes.

Asked about his post, Daugherty told NewsGuard in a direct message: “NewsGuard is heavily biased toward Democrats and was wrongly funded by taxpayers during the Biden administration. Of course they’d try to justify voter fraud and the blatant theft of our republic by attacking figures like Elon Musk who merely want voters to prove who they are — which should be the bare minimum. The real victims are American citizens being disenfranchised, not lawmakers in blue states who prohibit a broad requirement of photo ID.”

Musk did not respond to an emailed request for comment on his post.

Actually: It is not illegal for poll workers in either state to ask for a voter’s ID. In fact, poll workers in both states are directed to ask for ID when a voter’s identity has not been verified during registration, state election officials said.

  • The New York State Board of Elections states on its website that first-time voters will be asked for an ID “if the Board is unable to verify a voter’s identity before Election Day.” In New York, election officials first attempt to verify voters’ identities using a driver’s license number or the last four digits of a Social Security number, according to the election board website.

  • The California secretary of state’s website says that people voting for the first time after registering by mail “may be asked to show a form of identification when you go to the polls” if they did not provide a driver’s license number, California ID number, or the last four digits of a Social Security number when registering.

Both states generally instruct poll workers not to ask other voters for ID. California’s 2026 poll worker training standards state: “Poll workers must not ask a voter to provide their identification unless the voter list clearly states identification is required.” New York City’s poll worker manual gives a similar instruction, saying, “Do not ask the voter for ID unless ‘ID required’ is next to their name in their voter records.”

  • However, these rules are not codified in state law, and they do not prohibit election officials from asking for IDs in all instances.

Zooming out: Musk has donated almost $91 million to boost Republicans ahead of the midterms, Business Insider reported.

Editor’s Note: This story was updated to include more context on state rules for poll workers and comment from Eric Daugherty.


Partner Recommendation

Learn more about how to determine facts from fiction online with free newsletters from the News Literacy Project, a nonpartisan education nonprofit. For educators, The Sift® comes weekly with ready-to-go classroom resources like guides, quizzes, slides, discussion questions and teaching tips. For parents and families, Scroll Smarter is a monthly newsletter that provides quick, helpful tips to make sense of today’s information overload.


This newsletter was edited by Sofia Rubinson and Eric Effron.


Reality Check is produced by co-CEOs Steven Brill and Gordon Crovitz, and the NewsGuard team.

We launched Reality Check to shed light on the false claims spreading online, how they spread, and the forces behind them. Each day, we aim to bring you the story behind your news feed and help you stay informed about the false claims circulating in the news. Support our work by becoming a premium member.

Have feedback? Send us an email: realitycheck@newsguardtech.com.

Share NewsGuard’s Substack


Read the whole story
LeMadChef
4 days ago
reply
Can I have laudanum back? At least maybe some OG cola with cocaine in it.
Denver, CO
acdha
5 days ago
reply
Washington, DC
Share this story
Delete

I’m Kind Of Smitten With These Early Two-Cylinder Two-Stroke Suzuki Jimnys

1 Share

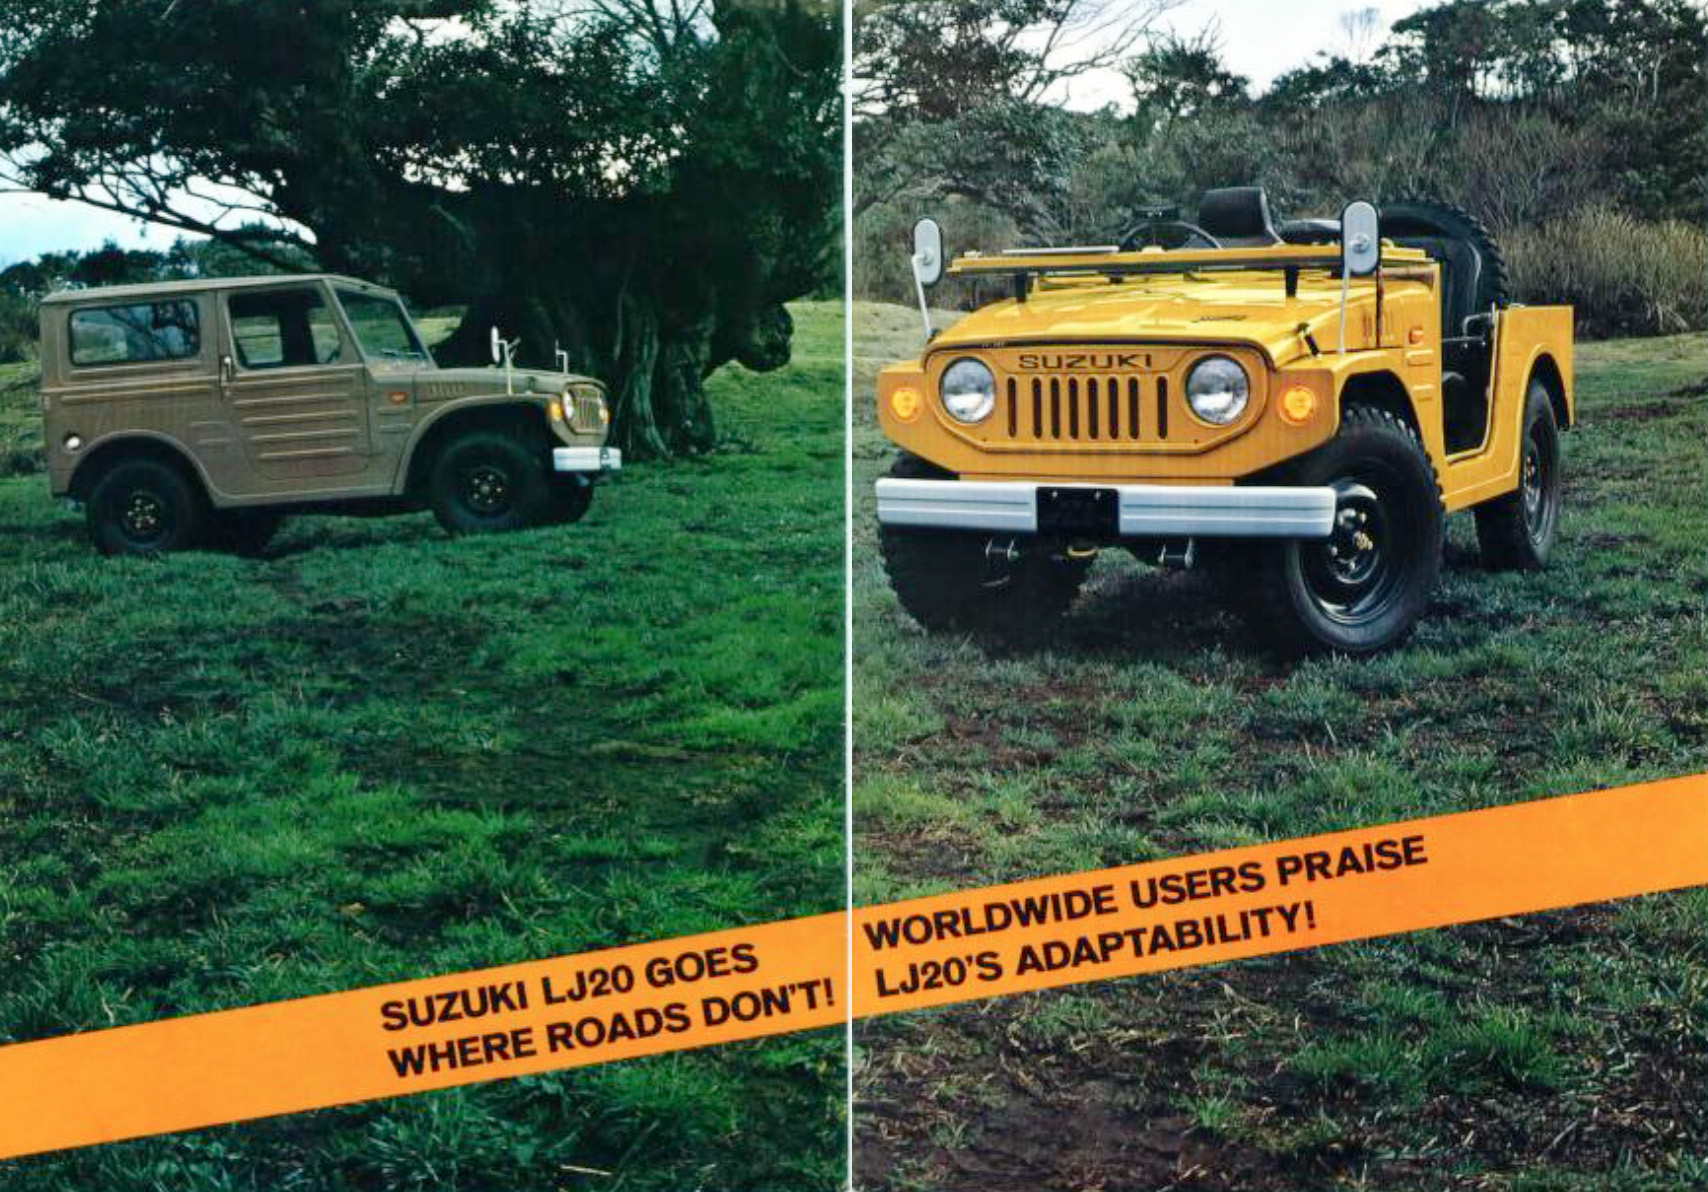
You know how I draw cars for Autopian members on their birthdays? Or close-ish to their birthdays? Well, I do and it’s just another perk of that incredible state of being we call Autopian Membership. Anyway, one of the ones I just did was a request for a Suzuki LJ20. I was aware of these before, in a vague way, but once I really started looking at them, I was hopelessly smitten.

The LJ series – which stood for Light Jeep, another reminder of how the term “jeep” was on the path to genericization, like Kleenex or Hoovering in the UK – was the start of the series that most of the world knows as the Jimny.

These early LJ series of Jimnys, introduced in 1970, seriously minimal. Jimnys have always been Kei-class, but back in 1970 that meant 360cc engines and under 10 feet of length. The early LJ10s had a two-stroke, two-cylinder air-cooled engine making 24 horsepower, good for 50 mph even with the off-road focused gearing. The thing only weighed 1290 pounds, after all.

Cs Lj20 1

Check out this great cowboy-inspired commercial from when they came out:

These two-stroke engines also had an oil injection system so you didn’t have to mix your oil and gas, like some sort of filthy animal. Later, Suzuki switched to a liquid-cooled engine for their LJ20, which got a power bump to a ravenous 28 hp.

Here’s a nice walkaround of one of those:

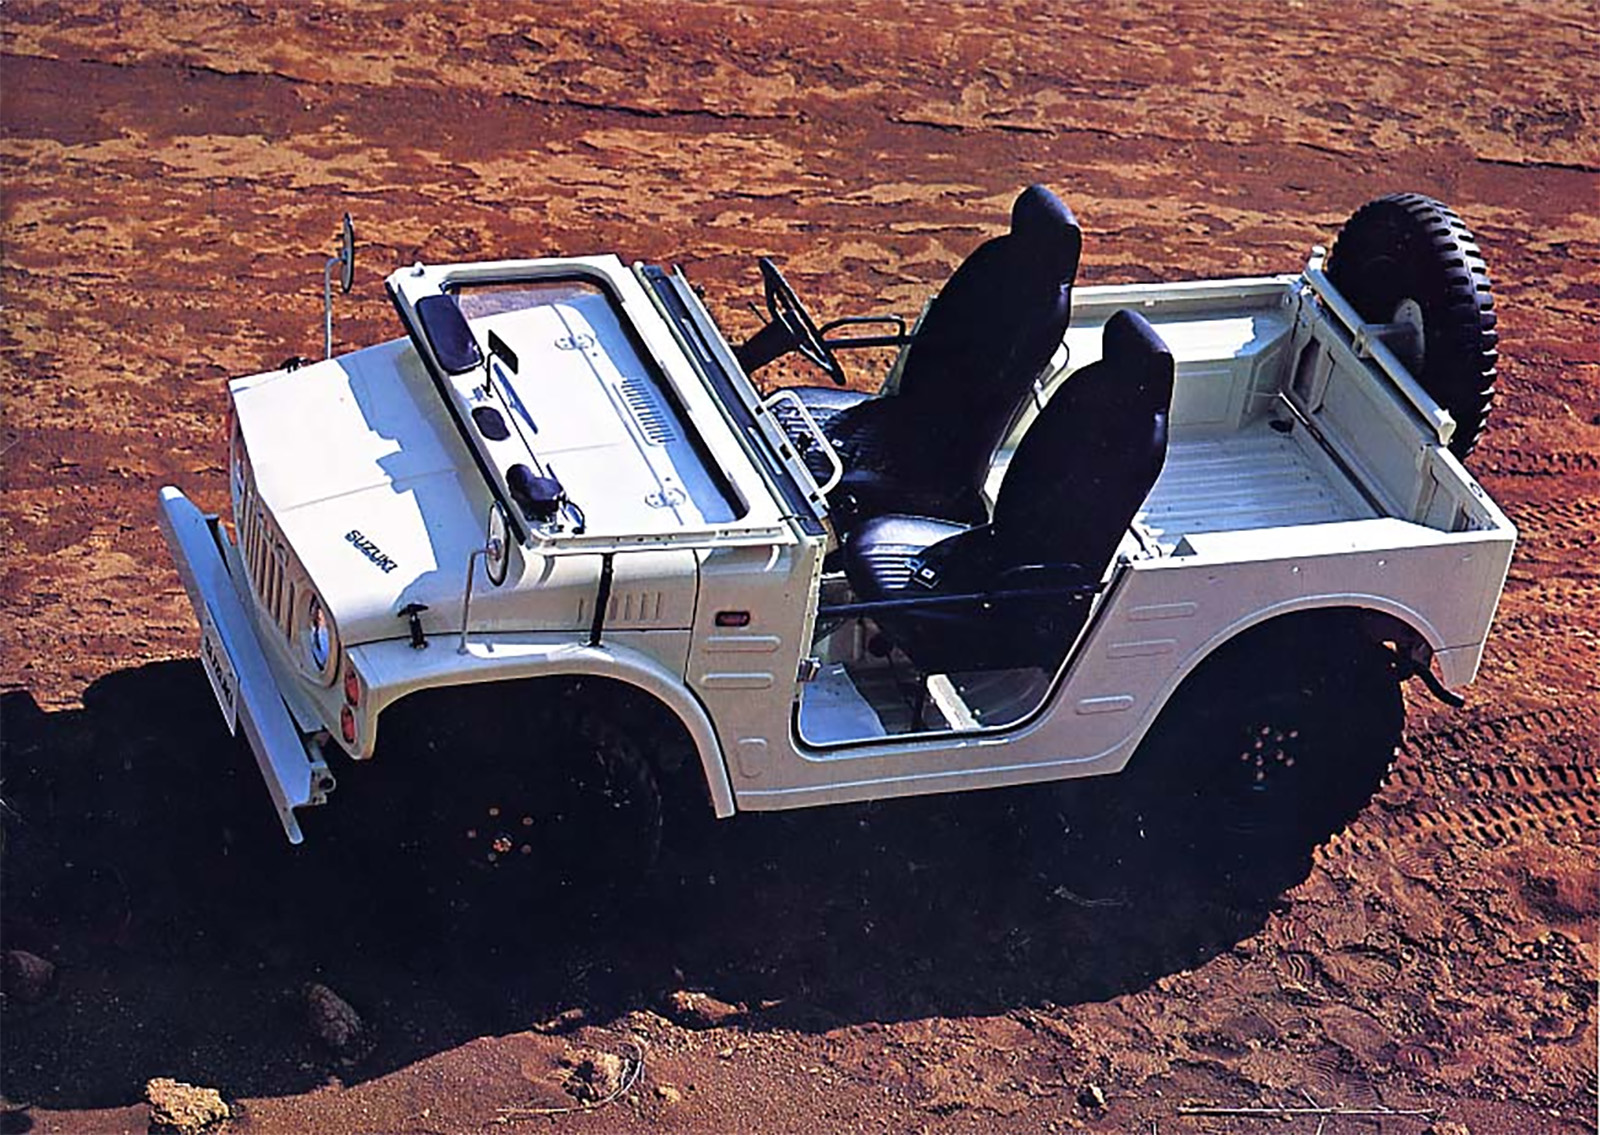
I suppose if anything, these Jimnys really showcase what a good design the basic original Bantam/Willys/Ford army Jeep was, because this is essentially a scaled-down version of that.

Cs Lj Overhead

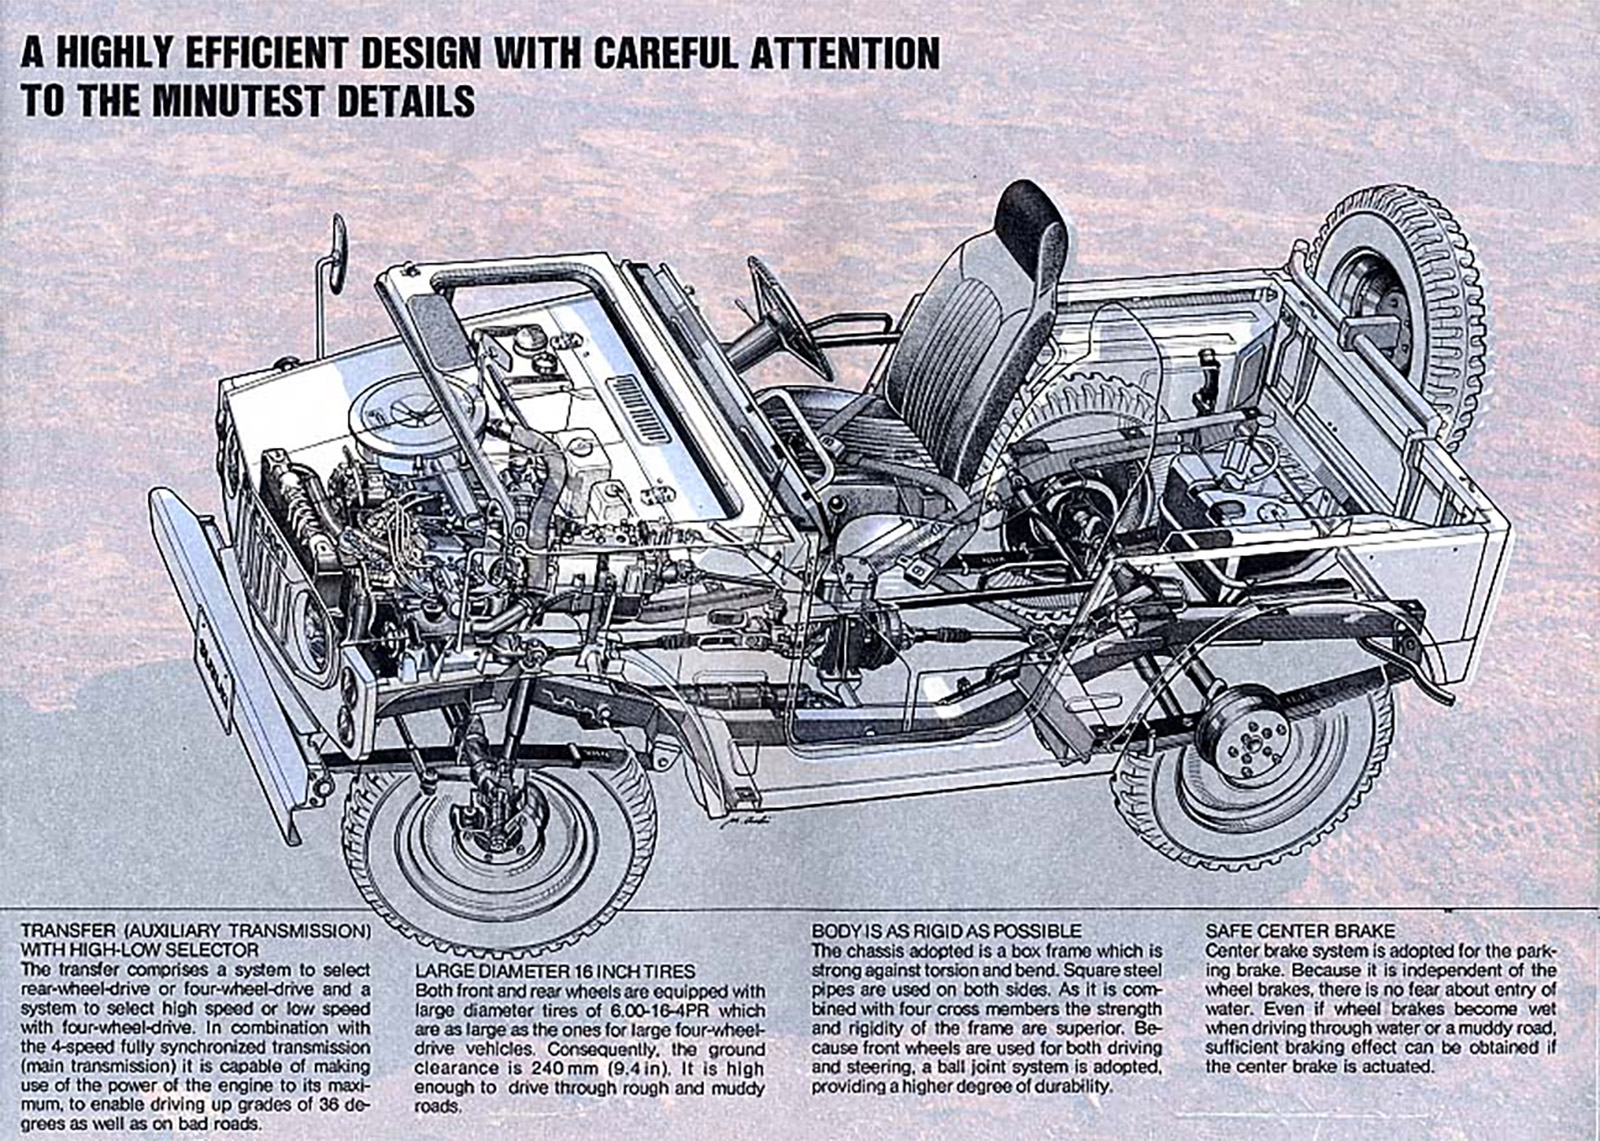
A little boxy tub on wheels, basically, with some seats and an engine bolted in. But it all just works! For moving two people and some cargo around rough terrain, it’s pretty hard to beat. Here, squint really hard at that picture up there and let’s see if we can see through it a bit:

Cs Lj Cutaway

Hey you did it! Great job! As you can see, it’s pretty straightforward Jeep-type engineering under there, ladder frame and leaf springs and solid axles, just all scaled down.

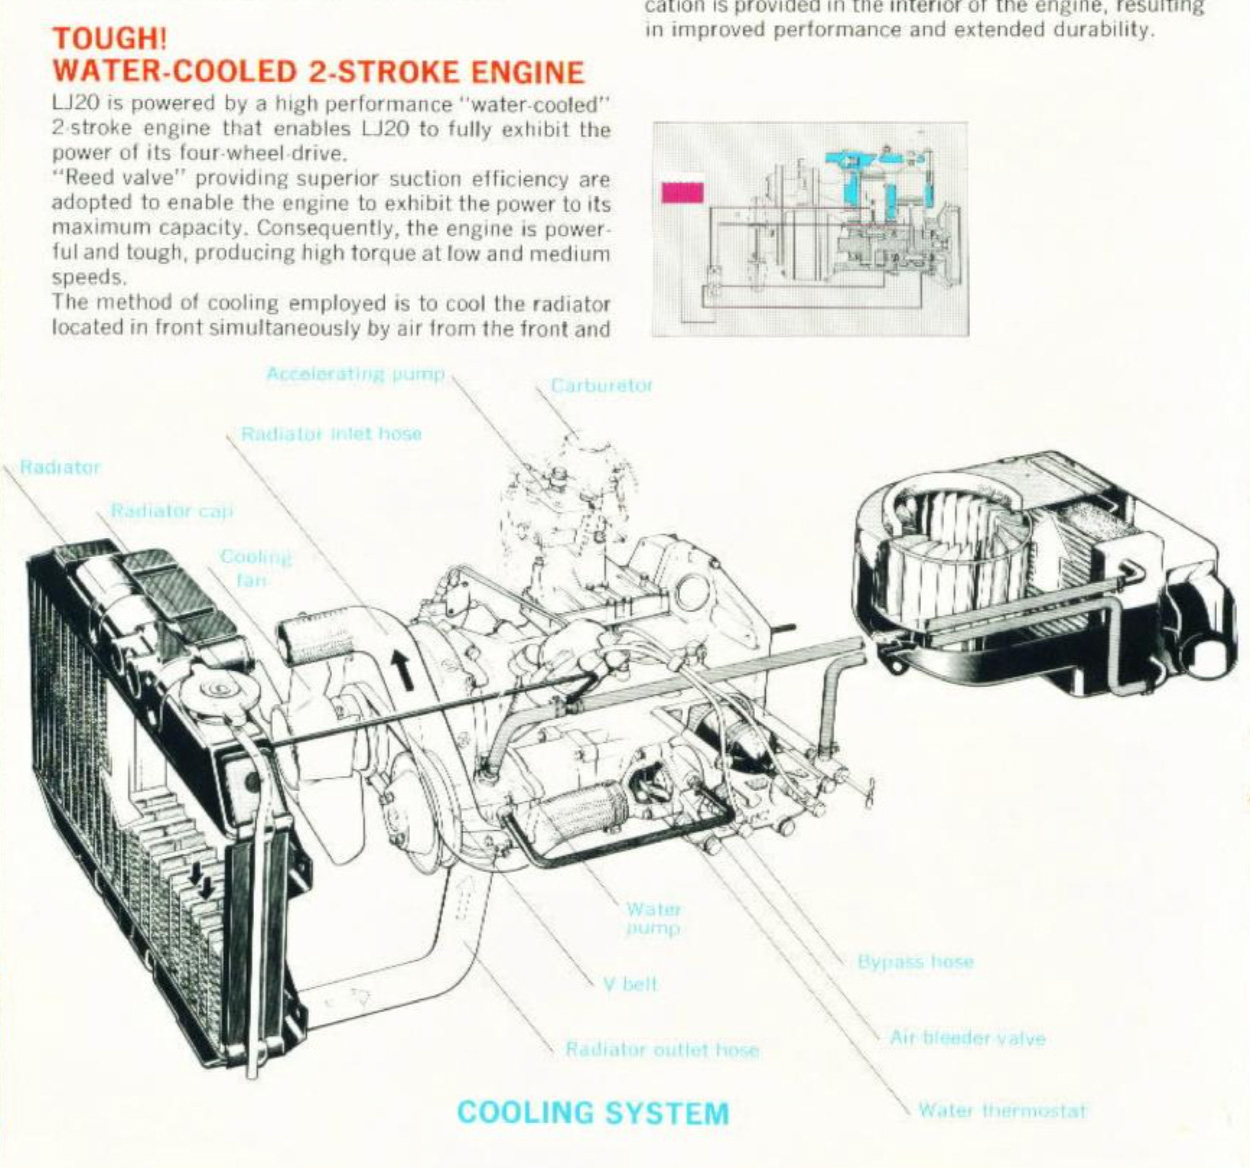
Cs Lj20 Cooling

Suzuki’s brochures get pretty technical, including things like this diagram of the new liquid-cooling system for the LJ20. Look how tall that carb stands on an otherwise pretty compact and low engine!

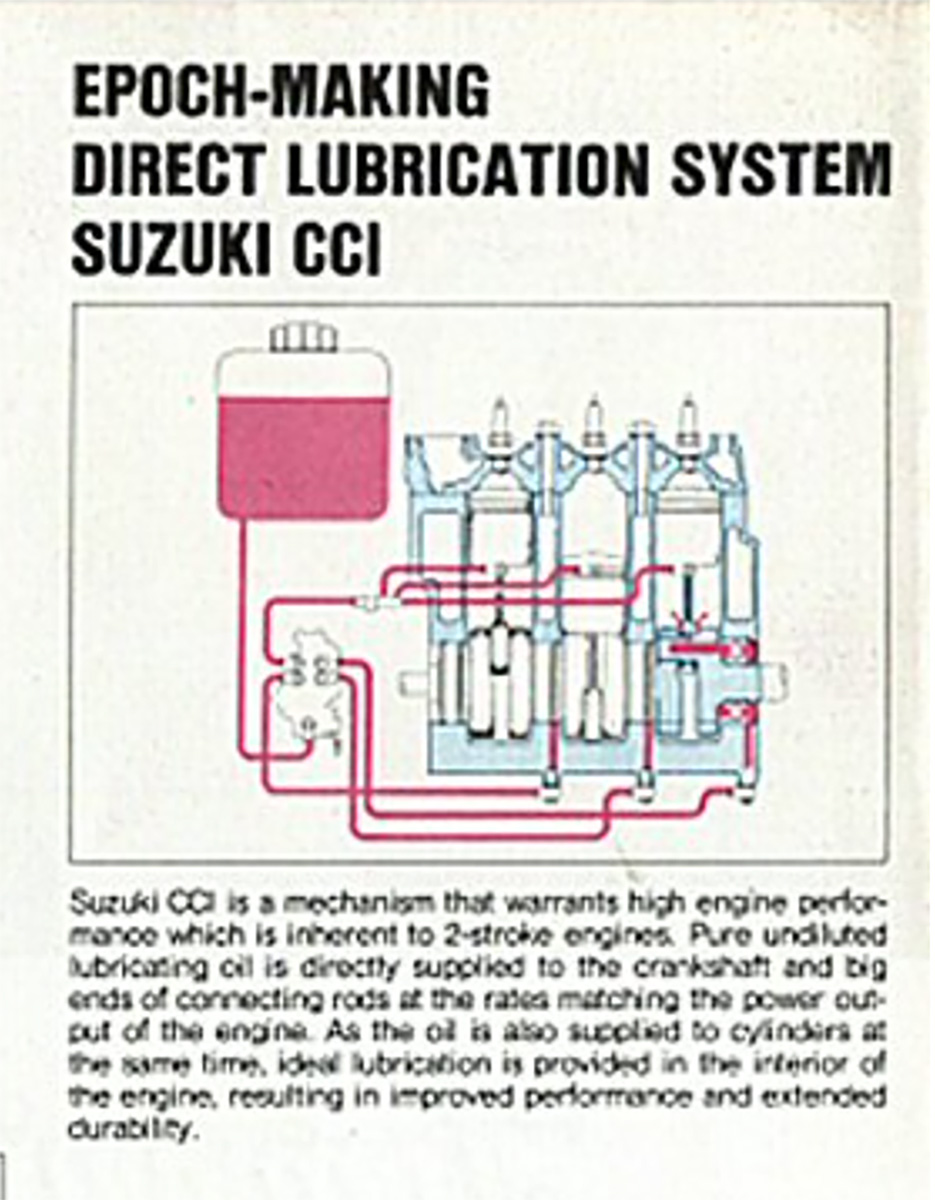
Cs Epoch Lj

Suzuki did get a little hyperbolic with some of their technical details, too. Like, sure, the CCI oil injecting system is great, but is it really “Epoch-making?” That feels a little too much. An epoch is a pretty big deal. We don’t call the last quarter of the 20th century the Suzuki CCI Epoch, after all.

They also were a bit hyperbolic with this description of the interior:

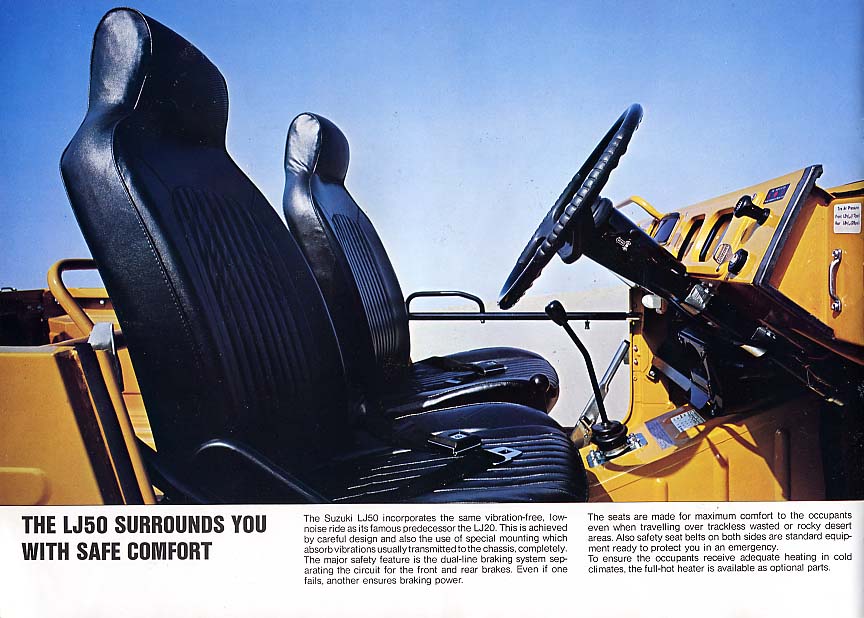
Cs Lj Interior

“Surrounds you with safe comfort?” I’m not sure I really believe any of those words. That interior is barely surrounding anything. It’s almost just two exposed seats on a platform. I’m sure those seats are comfortable enough, but this ain’t no Lincoln. And safe? An open 1970s Kei-class car is only safe if you run it into a wall of marshmallows or something.

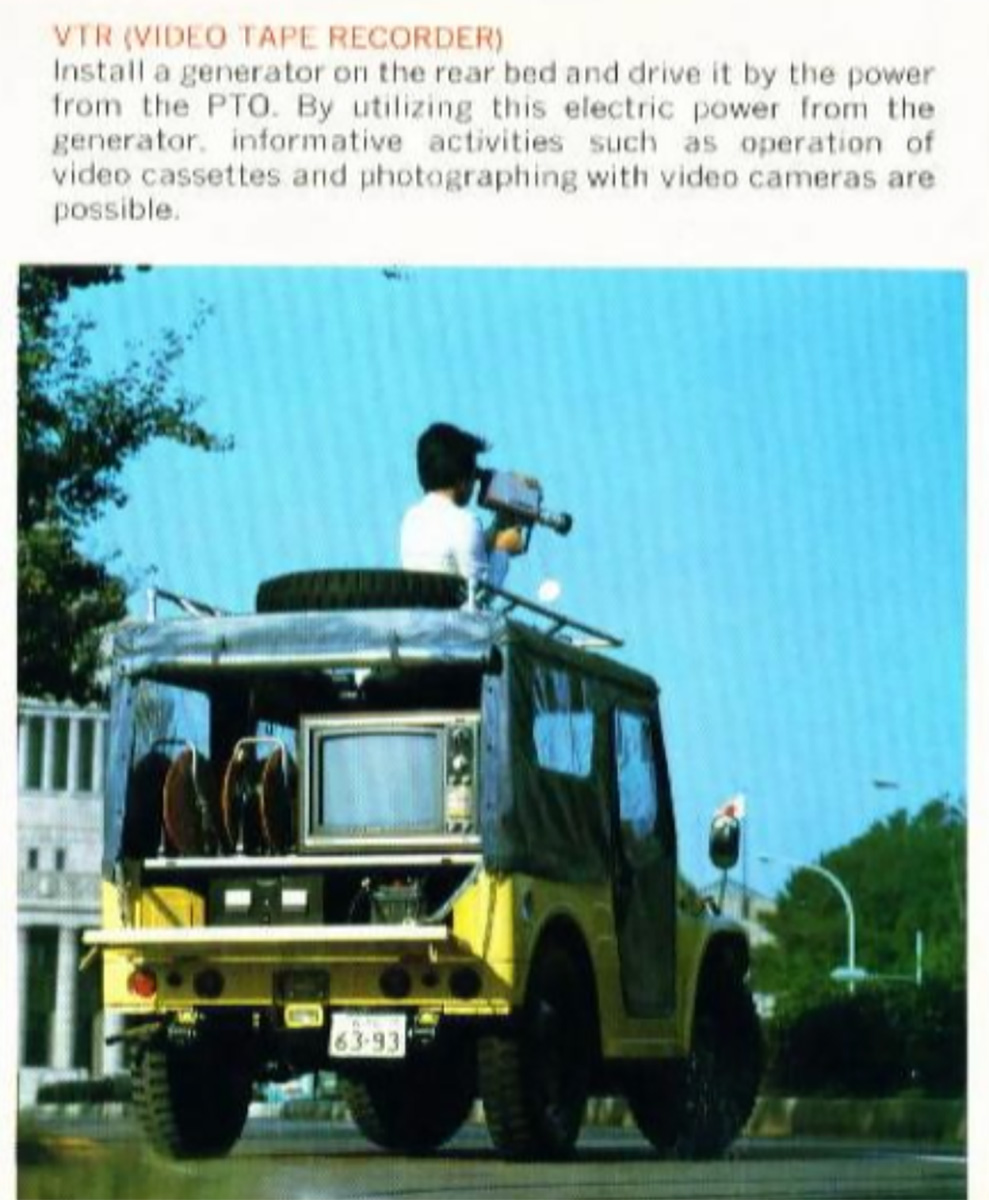
Cs Lj20 Vtr

The brochure also listed some interesting examples of how to outfit and use these LJs, including the usual pumping and hauling and fire service kinds of things. I was surprised to see this one, showing a whole camera/video tape rig in there. They mention it all running from the generator, which feels like a lot, but maybe? Those big CRTs did kind of slurp power.

Also, look at those spools of cable! And just how big all that stuff is! Your phone’s video recording abilities likely eclipse anything all this hardware could do.

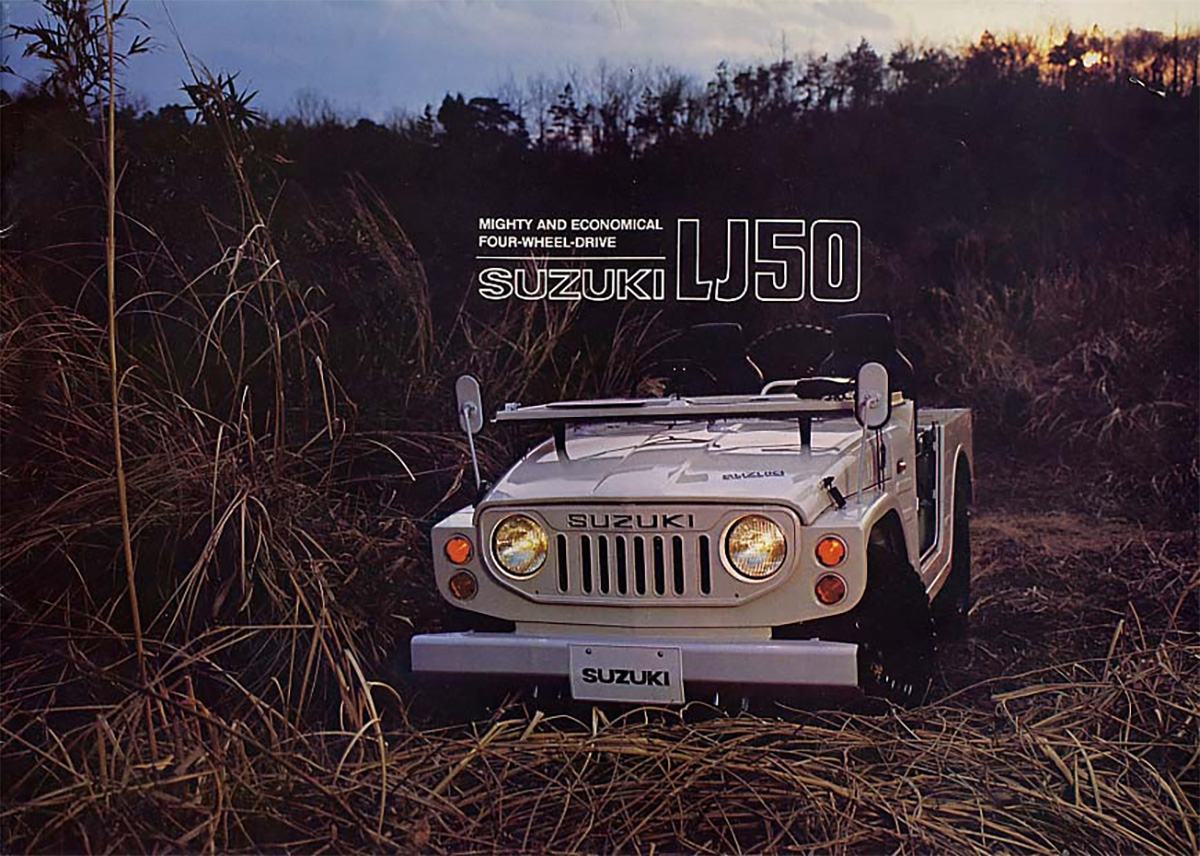
Cs Lj50

Anyway, thanks for letting me share my daily obsession. I’d love to try and drive one of these early Jimnys; It’d be fun to take one out on some trail with David in his DIY WWII Jeep and see how it compares!

The post I’m Kind Of Smitten With These Early Two-Cylinder Two-Stroke Suzuki Jimnys appeared first on The Autopian.

Read the whole story
LeMadChef
4 days ago
reply
Denver, CO
Share this story
Delete

111CS Build: Unveil

1 Share

We unveiled the 111CS at the Lotus United Gathering in Salt Lake City to a crowd of Lotus fanatics!  It was well received and the community was full of questions!

Read the whole story
LeMadChef
4 days ago
reply
Denver, CO
Share this story
Delete

Western Colorado coal mine violates methane caps nearly 4 times over, state says

1 Share
Alleged breaches at West Elk mine are so “wild” they should trigger Clean Air Act mandates to change mine operations and equipment, environmental groups say
Read the whole story
LeMadChef
4 days ago
reply
Denver, CO
Share this story
Delete

US being left behind in EV charging speeds as China goes sub-5 min to 70%

1 Share

Hype merchants have a habit of overdoing it, but there’s no denying that China is making the US look more than a little antiquated when it comes to electric vehicles. Some of that is due to a deep integration of connected services and an extension of the car as part of the owner’s digital life—think additional infotainment screens and AI personal assistants, but with an Android phone-maker’s cadence of updates rather than that of a traditional car company. Other advances sound more appealing. China’s OEMs are in a battle over who can charge the fastest, and this week, Geely fired its latest salvo.

China might have a much younger driving culture than North America or Europe, but it has still been long enough to condition those drivers to how long it takes to fill a tank of gas. For all their many improvements over internal combustion engine vehicles—far greater efficiency, instant torque, very little NVH, more reliabiity, and so on—EVs do still take longer to recharge than it takes to refuel a car with a liquid.

At least until now, it seems.

Geely’s new battery can charge at up to 2.2 MW and will recharge from 10 to 70 percent in 4.5 minutes. A 10–98 percent charge takes 8 minutes and 40 seconds. Predictive thermal management is done through AI, with an average pack temperature of 55˚C and a peak temperature during charging of 65˚C, Geely said.

And while you might think pumping large amounts of energy into a battery quickly and repeatedly could harm its health, Geely says that, using AI, the system applies micro pulses of current to “reactivate lithium ions accumulated at the negative electrodes during repeated fast charging,” extending battery life by 20 percent. The pack has been tested in both the Zeekr 001 and Lynk and Co 10—maybe we'll see a Volvo or Lotus use the same tech someday.

The numbers eclipse those from BYD, which debuted a new product in March that can charge from 10 to 70 percent in 5 minutes and 10 to 97 percent in 9 minutes. But CATL still looks like it’s on top; in April, it announced an LFP battery that can charge from 10 to 80 percent in 3 minutes 44 seconds, or from 10 to 98 percent in 6 minutes and 27 seconds.

In the US, the most powerful car chargers deliver a modest fraction of those megawatt outputs. All but the newest Tesla Superchargers top out at 250 kW and 400 V; in the 800 V world, Electrify America maxes out at 350 KW, IONNA’s new machines are rated for 400 kW, and ChargePoint has a 600 kW charger on the market.

Meanwhile, our electric vehicles lag in their charging speeds. Hyundai and Kia’s popular range of 800 V EVs (including the Ioniq 5 and EV6) will actually max out around 240 kW on an 800 V DC fast charger, and Porsche’s Taycan will only accept up to 320 kW, not all 350. The latest wave of 800 V German EVs like the BMW iX3 and Porsche Cayenne are now arriving with 400 kW DC charging capabilities.

Megawatt charging in the US is still the preserve of heavy-duty EVs—buses, semis, and the like; ChargePoint told Ars recently that “if you take two Express solos [its new 600 KW charger] and join them with a common DC bus, you now can deliver 1.2 megawatts through one port,” said ChargePoint CEO Rick Wilmer.

“Now, obviously, a NACS connector or a CCS1 connector won't handle that much power, but an MCS connector will. So that's all part of the roadmap for the Express architecture, with the Solo being the first product off that architecture,” he said.

Read full article

Comments


Read the whole story
LeMadChef
4 days ago
reply
Denver, CO
Share this story
Delete
Next Page of Stories